Does your website or app need a privacy policy? What Indian law requires
Last updated: 2 October 2026
Yes, in almost every case. A business whose website or app collects personal information must publish a privacy policy under the 2011 rules made under the Information Technology Act, which stay in force until 13 May 2027. From that date the Digital Personal Data Protection Act, 2023 applies in their place, and it requires a plain-language notice whenever consent is asked for, not only a policy page.
At a glance
- Applies to
- Any business whose website or app collects personal data from people in India, including a business abroad that offers goods or services here
- Law and rule
- Information Technology Act, 2000, section 43A, and the 2011 Rules, rules 4 and 5; Digital Personal Data Protection Act, 2023, sections 5 to 7; Digital Personal Data Protection Rules, 2025, rule 3
- Key dates
- Rules notified on 13 November 2025. Notice and consent duties apply, and the 2011 Rules fall away, on 13 May 2027.
Almost every business website collects some personal information: a contact form, a newsletter sign-up, analytics that track visitors, accounts, payments. Each of these brings the site within India's data protection rules. The more useful question is what the policy has to say, and that changes on 13 May 2027.
The current requirement under the IT Act
Under the Information Technology Act, 2000 and the Information Technology (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011, a body corporate that collects, receives, stores or handles personal information must publish a privacy policy on its website. "Body corporate" covers companies, firms, sole proprietorships and other associations engaged in commercial or professional activities. The policy has to be clear and easily accessible, and must set out:
- the types of personal and sensitive personal data collected
- the purpose of collection and use
- when and to whom the information may be disclosed
- the reasonable security practices followed
The rules also require a grievance officer to be designated for complaints about how information is handled, with the officer's name and contact details published on the website.
What changes under the DPDP Act
The Digital Personal Data Protection Act, 2023 replaces this framework with a broader one. It applies to digital personal data processed in India, and to processing outside India connected with offering goods or services to people in India. The Digital Personal Data Protection Rules, 2025 were notified on 13 November 2025 and bring the Act into force in three stages.
| Date | What applies | Effect on a privacy policy |
|---|---|---|
| 13 November 2025 | The Data Protection Board of India and the provisions that set it up | None yet. The 2011 Rules continue to apply. |
| 13 November 2026 | Registration of Consent Managers | None, unless the business plans to use a Consent Manager. |
| 13 May 2027 | Notice, consent, security, breach reporting and the rights of individuals | The notice must meet the Act and rule 3. Section 43A of the IT Act and the 2011 Rules cease to apply. |
The DPDP Act works through notice and consent. Every request for consent must come with, or follow, a notice that explains in clear and plain language:
- the personal data to be processed and the purpose
- how the person can withdraw consent and exercise their rights
- how to complain to the Data Protection Board of India
Rule 3 adds that the notice must be understandable on its own, without reference to other documents, and must give an itemised description of the personal data and the specific purpose. A person must be able to read the notice in English or in any of the languages listed in the Eighth Schedule to the Constitution.
Where a business already holds data collected on consent given before the Act applies, it must send the same notice as soon as reasonably practicable. An existing mailing list or customer database therefore needs attention too, not only new sign-ups.
In practice, a single privacy policy page is no longer the whole answer. Businesses also need notices where data is collected, a way to record and withdraw consent, and a process for handling requests from users.
When consent is not needed
Section 7 of the Act lists "legitimate uses" for which a business may process personal data without asking for consent. Those most relevant to a website are:
- data a person gives voluntarily for a specified purpose, where they have not said they object, such as an enquiry sent through a contact form, used to answer that enquiry
- processing needed to comply with a law or a court order
- processing for the purposes of employment
Using the same data for something else, such as adding an enquirer to a marketing list, falls outside the legitimate use and needs consent.
Other reasons a policy is required
- App stores. Both the Google Play Store and the Apple App Store require apps to link to a privacy policy.
- Platforms. The intermediary rules of 2021 require a platform that hosts user content to publish its rules, privacy policy and user agreement.
- E-commerce. The Consumer Protection (E-Commerce) Rules, 2020 require e-commerce entities to display information including grievance redressal details.
- Users abroad. A website with users in the European Union may also need to meet the transparency requirements of the GDPR.
- Payment providers and partners. Payment gateways and business customers commonly ask for a privacy policy during onboarding.
The risk in a copied policy
A privacy policy is a statement of what a business actually does with data. A policy copied from another website, or generated from a template, often describes data collection that does not happen and misses collection that does, such as analytics tools, third-party chat widgets or data shared with a payment provider. That mismatch is a problem in itself: it misleads users, and it is one of the first things a regulator, investor or business customer will notice.
A useful policy starts from an audit of what the website or app collects, why, where it is stored and who it is shared with. The policy, the consent flows and the internal processes should then all describe the same thing.
Common mistakes
- Wording from the 2011 Rules only. A policy built around "sensitive personal data or information" and "body corporate" will be out of date from 13 May 2027.
- Borrowed GDPR terms. "Controller", "processor" and "legitimate interests" come from European law. The DPDP Act speaks of Data Fiduciaries, Data Processors and Data Principals, and it has no general "legitimate interests" ground.
- No way to withdraw consent. The Act requires withdrawing consent to be as easy as giving it.
- No named contact. The policy should say who answers questions about personal data, and how to complain to the Board.
- A policy that does not match the site. Tools added after the policy was written, such as a new analytics or chat tool, are often missing.
A short checklist
- List every point where the website or app collects personal data, including tools and plugins.
- Record the purpose of each, and who else receives the data.
- Publish a policy that matches that list, in plain language.
- Add notices and consent where data is collected.
- Designate a contact for privacy requests and complaints.
- Review the policy whenever the product or its tools change, and before 13 May 2027.
Questions
For almost any business website or app that collects personal data, yes. The 2011 Rules under the Information Technology Act require a published privacy policy, and from 13 May 2027 the DPDP Act requires a notice before or when consent is asked for.
Yes. A name, an email address and a phone number are personal data, and a business that collects them falls within the rules. The policy for such a site can be short.
Section 43A of the Information Technology Act and the 2011 Rules continue to apply until that date. The notice and consent duties of the DPDP Act apply from then on.
Yes, where it processes digital personal data in connection with offering goods or services to people in India. Section 3 of the Act sets out its reach.
India has no law specifically about cookies. Cookies and trackers that identify a person collect personal data, and under the DPDP Act that needs notice and a lawful ground, which will usually be consent.
The Schedule to the DPDP Act allows the Data Protection Board to impose a penalty of up to ₹50 crore for a breach of the Act or the Rules that has no specific penalty of its own. Failing to take reasonable security safeguards carries a penalty of up to ₹250 crore.
Sources
1. The Information Technology Act, 2000, s. 43A.
2. The Information Technology (Reasonable Security Practices and Procedures and Sensitive Personal Data or Information) Rules, 2011, rr. 4 and 5(9).
3. The Digital Personal Data Protection Act, 2023 (Act 22 of 2023), ss. 3, 5, 6, 7 and 44, and the Schedule.
4. The Digital Personal Data Protection Rules, 2025, r. 3, and the commencement notification of 13 November 2025.
5. The Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, r. 3(1)(a).
6. The Consumer Protection (E-Commerce) Rules, 2020, r. 4.
Related services
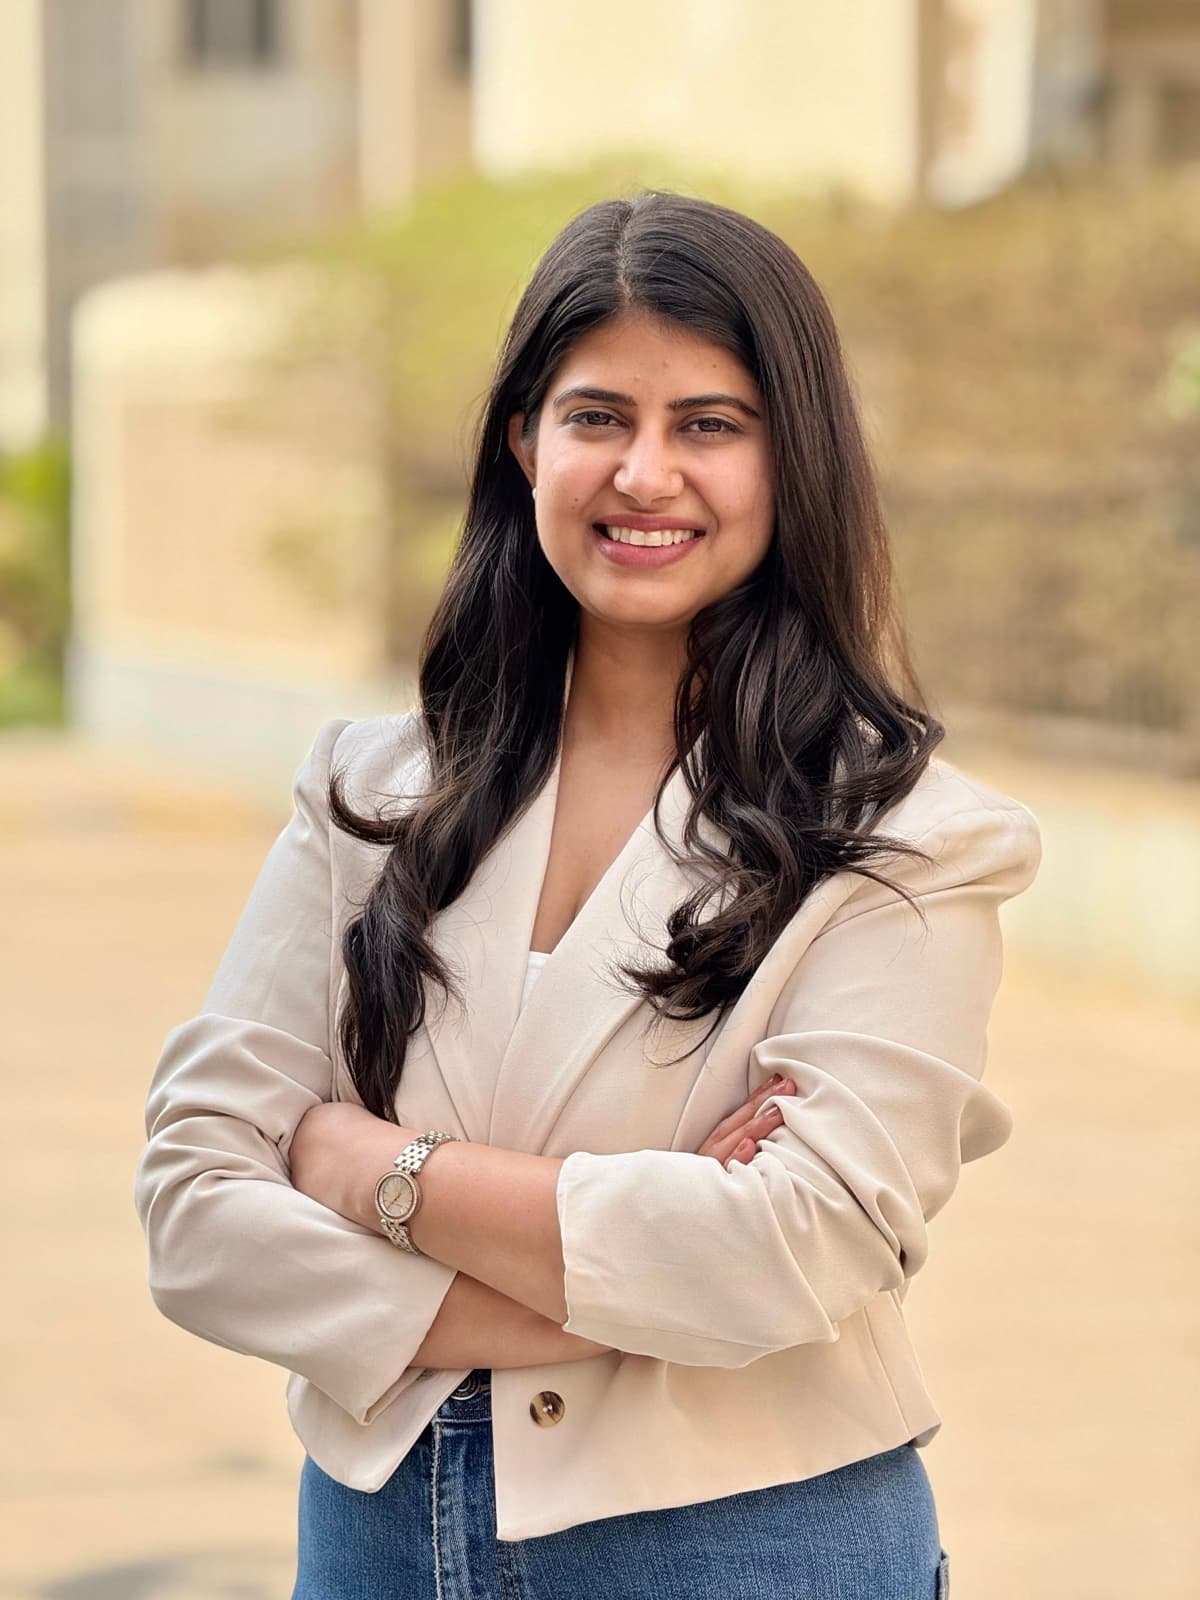
Written and reviewed by
Kanika Marwaha Bindal
Advocate, Gurugram. Postgraduate in Corporate Laws, NLU Jodhpur.
She trains Internal Committees and serves as an external member on POSH committees, and has advised clients in India, the UAE, the United States, Canada, Japan and Australia.